Cyber Security & Compliance
ISO 9001 Certified
|
ISO 27001 Certified
|
Cyber Essentials Certified
|
G-Cloud Supplier
|
ISO 9001 Certified | ISO 27001 Certified | Cyber Essentials Certified | G-Cloud Supplier |
Reduce Cyber Risk and Strengthen Resilience_
Valuecom helps organisations understand cyber exposure, strengthen security governance and meet compliance requirements.
We provide independent assurance and practical delivery support to improve controls, protect critical services and strengthen response and recovery capabilities.
Trusted Across Healthcare, Government & Regulated Environments_
Common Challenges
Increasing cyber security threats
Limited visibility of cyber risk
Complex regulatory and compliance requirements
Weak security governance and accountability
Gaps in security controls and resilience
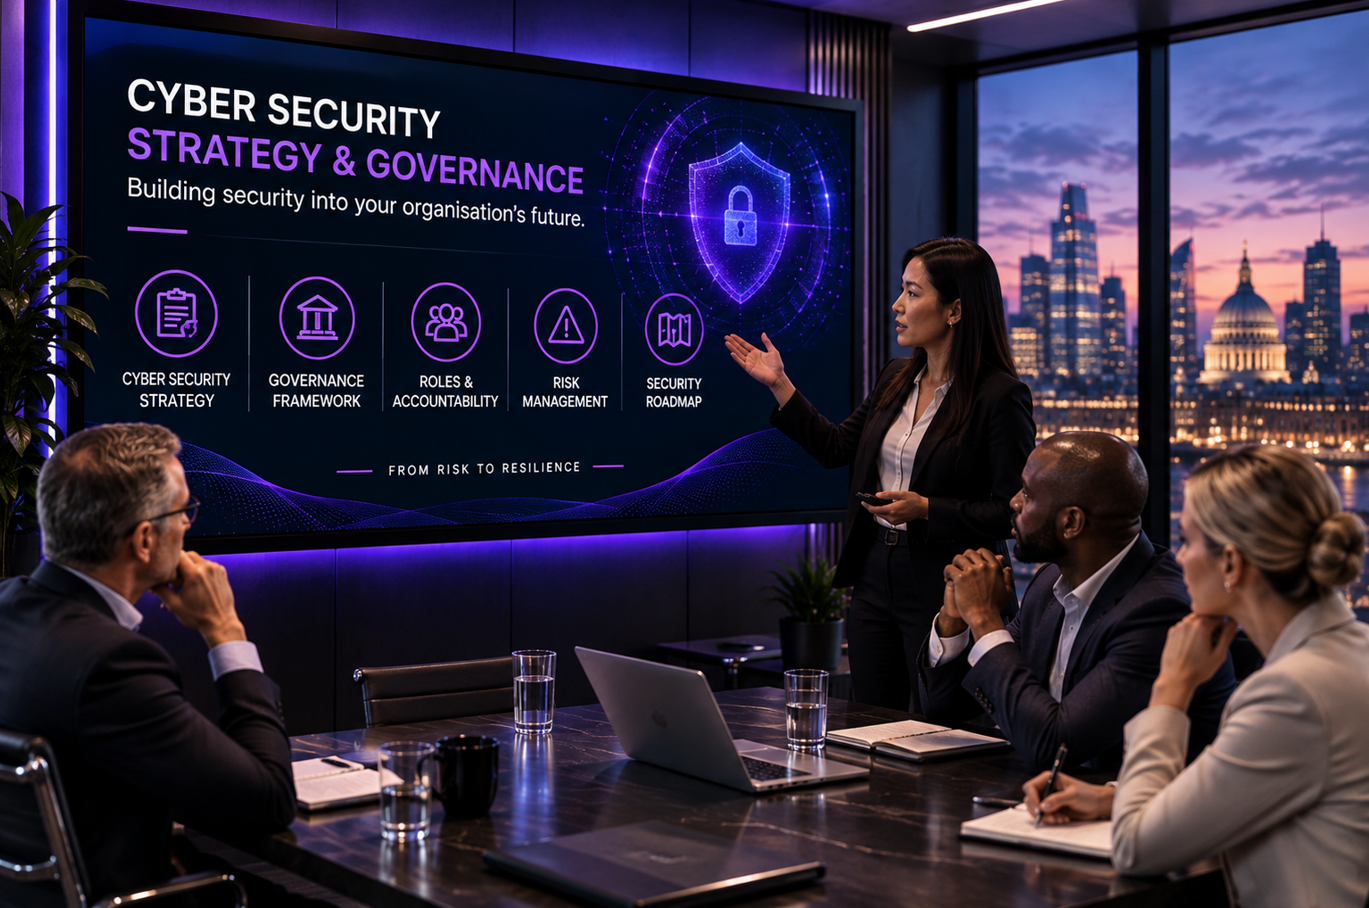
Cyber Security Strategy & Governance_
Define how cyber security is directed, governed and aligned to business risk.
Deliverables include
Cyber security strategy
Governance framework
Roles & accountability
Risk management
Security roadmap
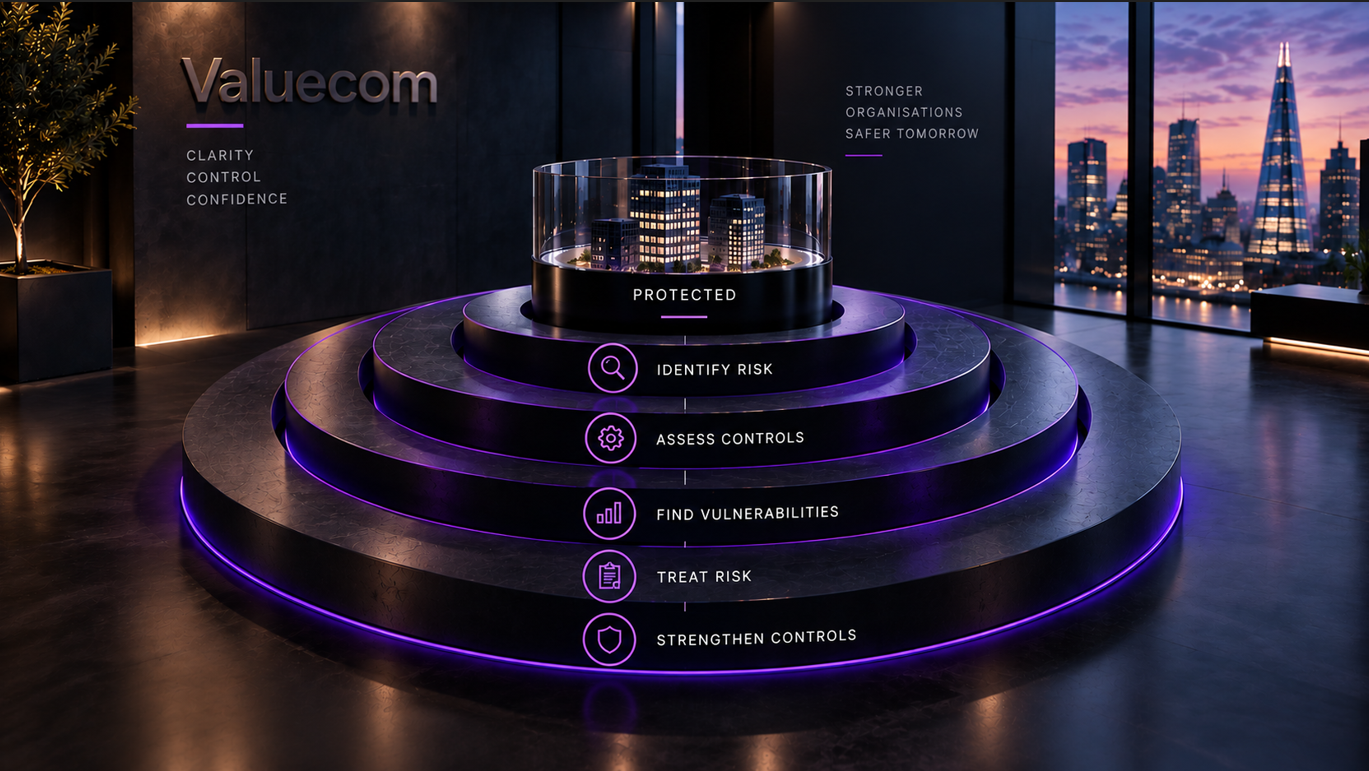
Security Risk & Controls_
Identify and reduce cyber risk through effective security controls and stronger protection.
Deliverables include
Cyber risk assessment
Security control review
Vulnerability assessment
Risk treatment planning
Control improvement roadmap
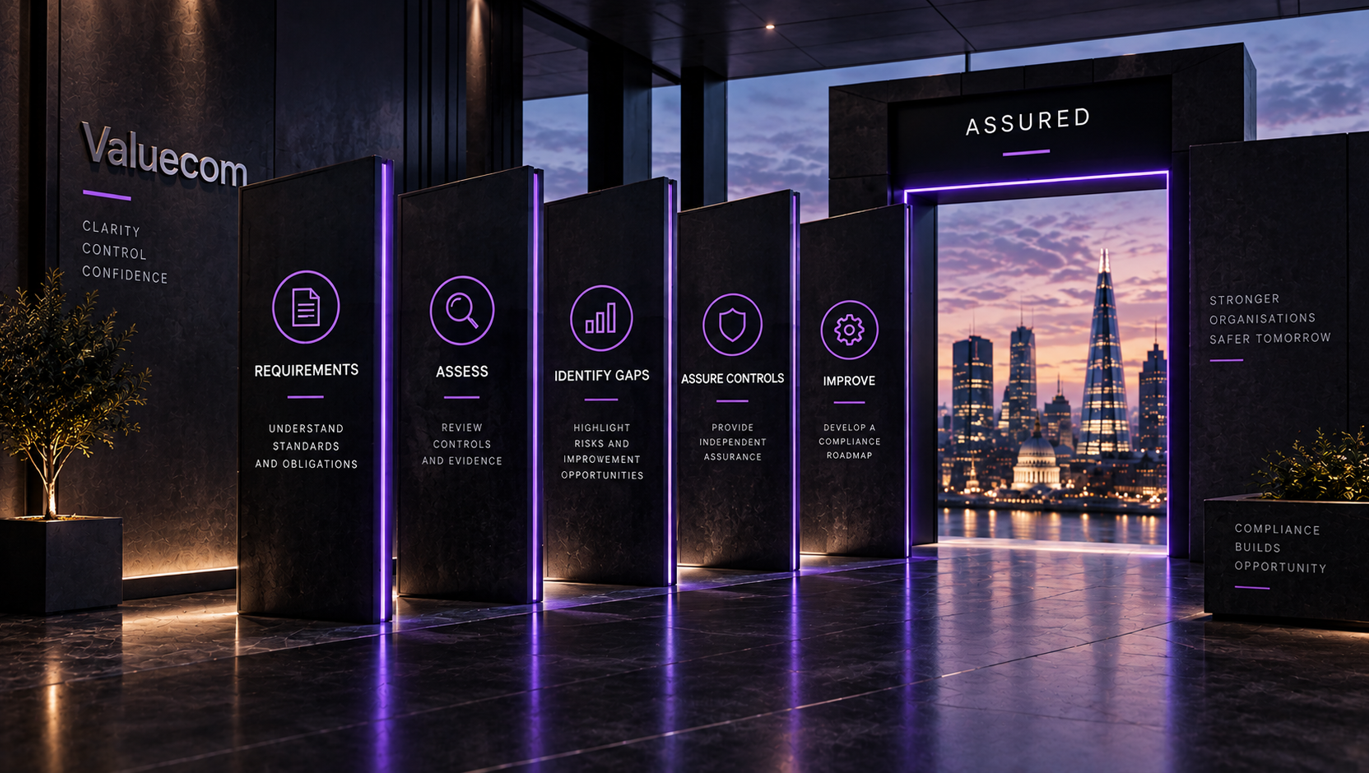
Compliance & Assurance_
Assess compliance, identify gaps and provide independent assurance against relevant standards and requirements.
Deliverables include
Compliance assessment
Regulatory gap analysis
Security framework alignment
Control assurance
Compliance improvement roadmap
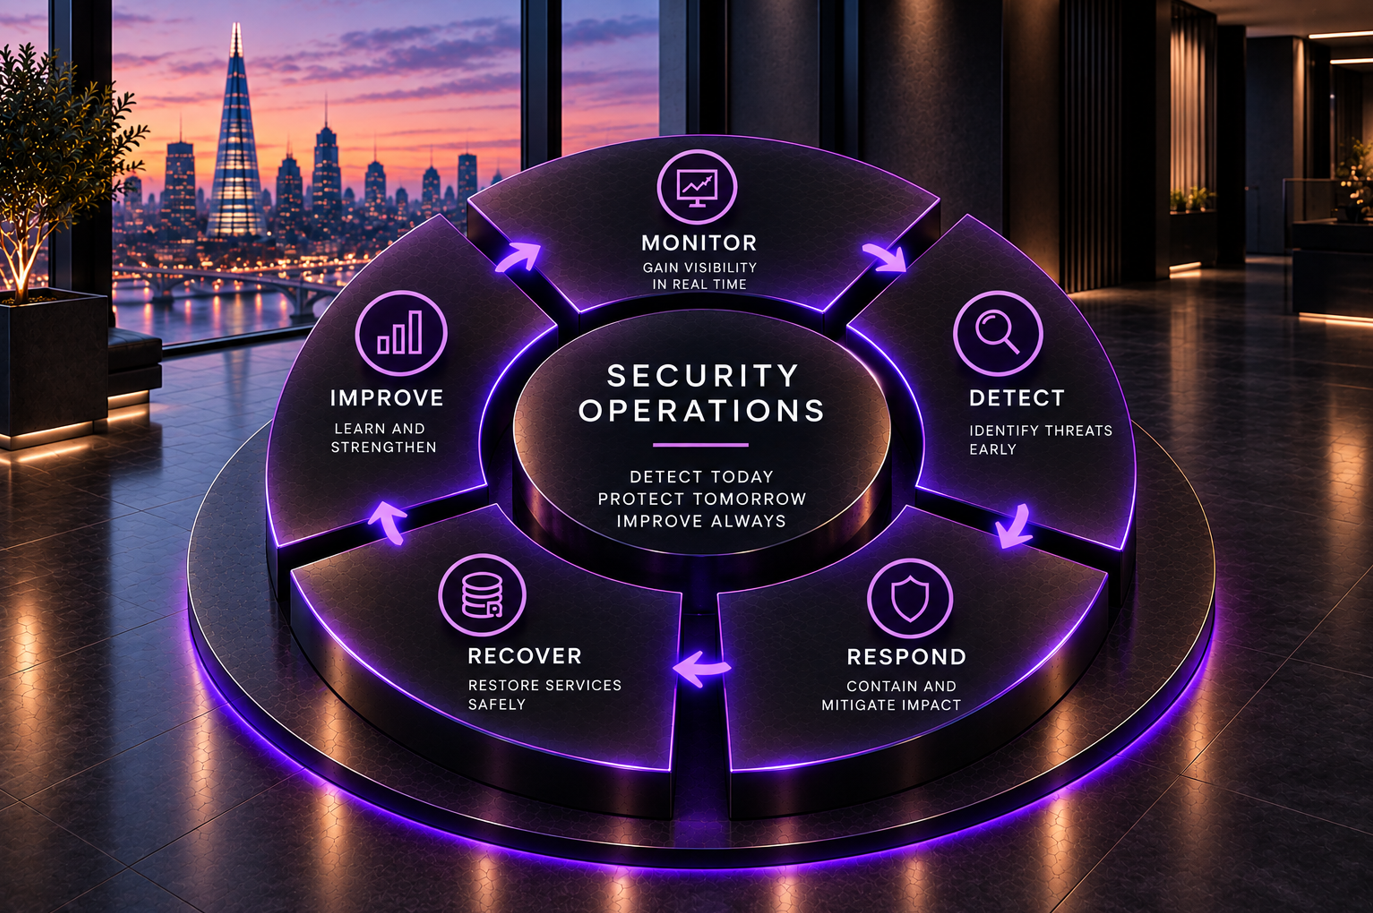
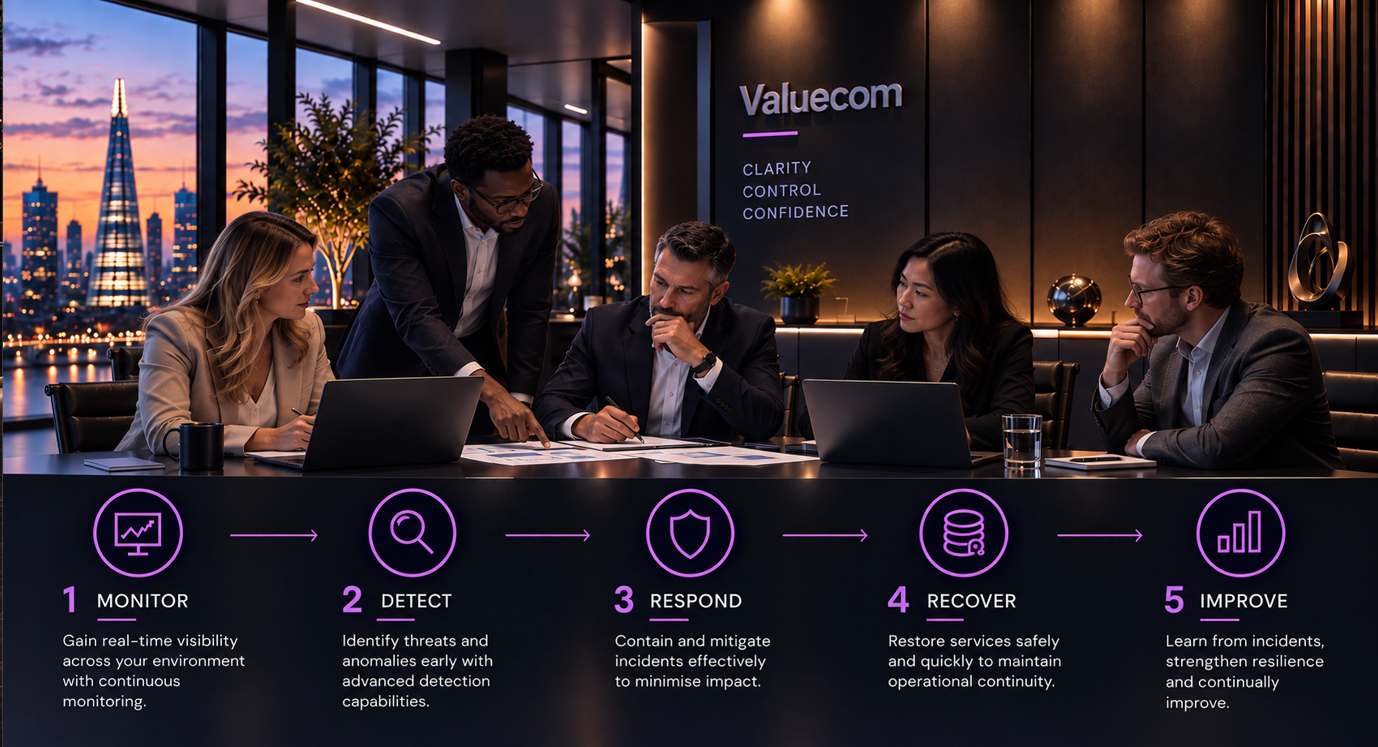
Security Operations & Improvement_
Strengthen operational security through effective monitoring, incident management and continual improvement.
Deliverables include
Security monitoring
Threat detection
Incident response
Security performance
Continual improvement roadmap
Our Approach_
Assess: Understand cyber risk, current controls, compliance requirements and priorities.
Define: Establish security objectives, governance requirements and target outcomes.
Protect: Strengthen security controls, reduce vulnerabilities and address priority risks.
Assure: Validate compliance, control effectiveness and organisational resilience.
Improve: Strengthen security operations, performance and continual improvement.
Typical Outcomes_
Clients engage Valuecom to achieve:
Reduced cyber security risk
Stronger security controls
Improved regulatory compliance
Greater visibility of cyber risk
Improved security resilience
Stronger security governance
Greater confidence in cyber security posture
Related Services_
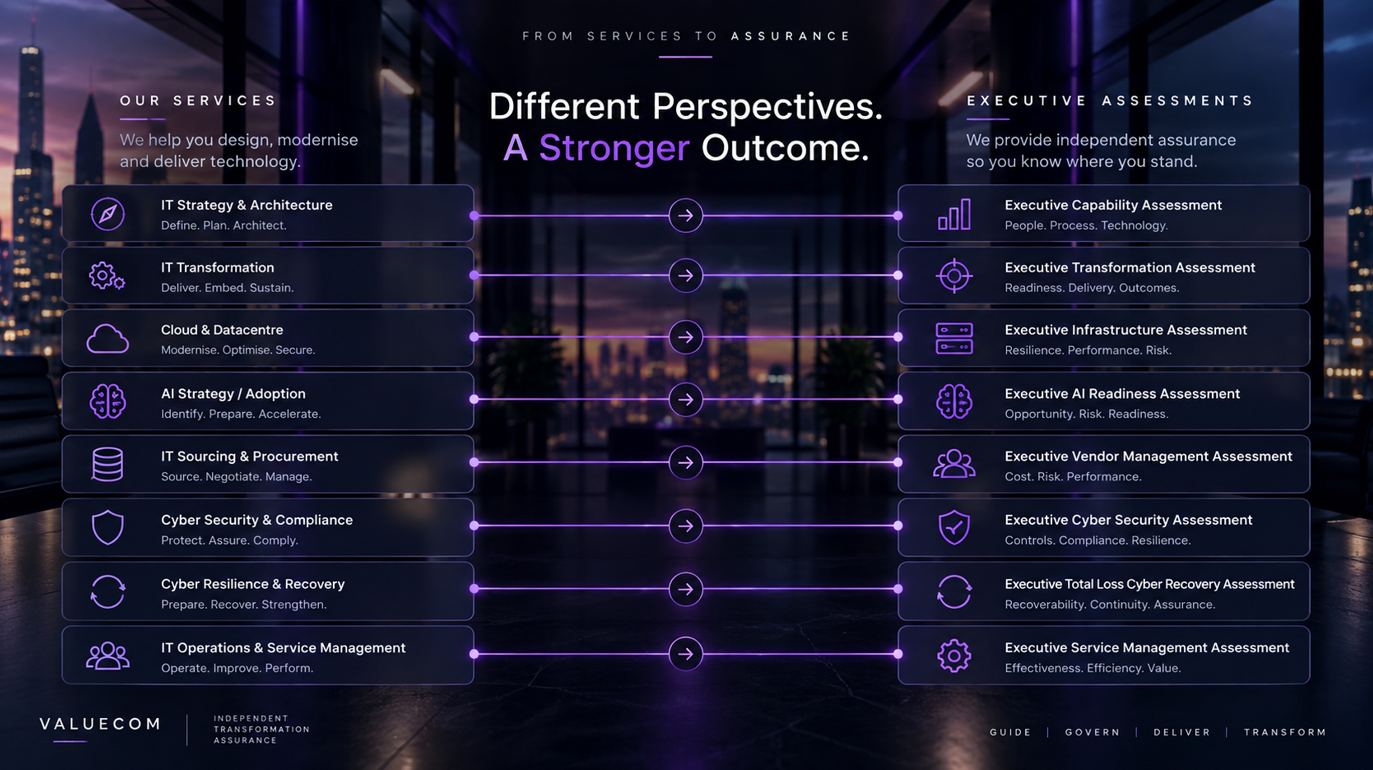
AI Strategy / Adoption (Coming Soon)
Cyber Resilience & Compliance (Coming Soon)
Related Assessments_